Service robot holding a tablet
--Days
--Hours
--Minutes
--Seconds

Organised by TecHive Association

The Agentic Systems Framework

Trust, Security, and Governance

Date: 21 January 2027 5:30 pm - 8:30 pm UAE Time Format: Virtual Event (Zoom)

A focused conference examining how organisations and institutions can responsibly adopt AI systems that are increasingly capable of making decisions, coordinating tasks, accessing tools, and taking autonomous action.

The event brings together senior leaders and experts from government and public institutions, enterprise technology, artificial intelligence, cybersecurity, governance, policy, research, and digital transformation to move from broad discussion of AI capability to responsible operational deployment, secure autonomy, institutional readiness, and accountable human oversight.

About the Event

Event Overview

The Agentic Systems Framework: Trust, Security, and Governance will examine the practical questions organisations face as AI gains greater agency: how much autonomy should AI have, what institutional foundations are required before deployment, how autonomous systems should be secured, and how accountability and meaningful human oversight can be preserved.

The practical challenge is not simply whether an AI agent can perform a task, but whether the surrounding organisation is prepared to deploy it responsibly: whether the data and technology foundations are ready, whether permissions and authority are clearly defined, whether the system can be monitored and contained, and whether meaningful human intervention remains possible.

Team collaborating around a laptopProfessionals in a strategy workshop
Technology professional working with a laptop in a data centre
Robot hand reaching forward

Why Agentic AI Matters

A new generation of agentic AI systems can plan tasks, coordinate activities, access tools and data, interact with software systems, and take actions within defined boundaries. This shift from assistance to action changes the question: no longer only what AI can generate, but what AI should be authorised to do, how much autonomy it should have, how its actions should be monitored, and how accountability should be maintained as decisions and actions are increasingly delegated to software agents.

Conference Objectives

Seven aims shape the programme, from how agents earn autonomy to how organisations keep them secure and accountable.

  • From assistance to action

    Examine the transition from assistive AI to agentic systems that can plan, coordinate, use tools, and take action.

  • Autonomy and decision authority

    Explore how organisations are assigning different levels of autonomy and decision authority to AI agents.

  • Institutional foundations

    Understand what it takes to operationalise and scale Agentic AI: data, workflows, infrastructure, skills, operating processes, and governance.

  • Security and resilience

    Examine the challenges that arise when AI agents can access data, tools, APIs, and operational systems.

  • Accountability and intervention

    Discuss how organisations define accountability, authority limits, human approval, auditability, and intervention mechanisms.

  • Lessons from real deployments

    Share implementation experiences, practical examples, emerging practices, and lessons from real-world Agentic AI adoption.

  • Cross-sector dialogue

    Bring together government, industry, technology providers, cybersecurity leaders, governance professionals, researchers, and institutional decision-makers.

Agenda Overview

The event will follow a focused programme structure designed to move from strategic context-setting to three thematic discussions, followed by audience interaction and closing reflections.

01

Opening Remarks and Conference Context Setting

1 Moderator

02

Opening Keynote

The Agentic Systems Framework: Trust, Security, and Governance

03

Theme 1

AI Autonomy & Decision-Making

2 Panelists (15 minutes each)

04

Theme 2

Security & Resilience of Autonomous AI

2 Panelists (15 minutes each)

05

Theme 3

Governance, Accountability & Human Oversight

2 Panelists (15 minutes each)

06

Interactive Live Q&A / Audience Discussion

07

Closing Reflections and Key Takeaways

Event Themes

The event is structured around three core themes, each examining a different dimension of responsible Agentic AI adoption and operation.

Humanoid robot facing the camera
01

Theme 1: AI Autonomy & Decision-Making

When should AI recommend, decide, or act?

Explore how organisations are using different levels of AI autonomy, from systems that recommend or support decisions to agents that can execute actions within defined boundaries. The discussion will examine emerging approaches to decision rights, human approval, escalation, traceability, and the distinction between what an AI agent can technically do and what it is authorised to do. It will also consider workflow readiness and system integration before greater decision authority is delegated to AI agents.
Illuminated circuit board schematic
02

Theme 2: Security & Resilience of Autonomous AI

How are organisations securing AI systems that can access tools and take action?

Explore the security challenges emerging as organisations deploy AI agents that can access data, invoke tools, call APIs, and initiate actions. The discussion will examine how organisations are approaching agent identity and authorisation, least-privilege access, secure integration, runtime monitoring, agent-specific threats, containment, recovery, and operational resilience, including the infrastructure readiness required for safe deployment at scale.

Leaders in a moderated discussion
03

Theme 3: Governance, Accountability & Human Oversight

How are organisations maintaining accountability and human oversight as AI gains greater agency?

Examine how organisations are approaching governance as AI agents take on increasingly active roles within operational environments. The discussion will explore emerging approaches to authority limits, accountability, human approval, runtime policy enforcement, auditability, continuous assurance, meaningful human intervention, governance-by-design, and the organisational processes required to operationalise these controls responsibly.

Engineer working with automation equipment

Across All Three Themes

Institutional Readiness

Institutional readiness is treated as a cross-cutting implementation consideration in every theme, examining what organisations need in place to operationalise and scale Agentic AI responsibly.

  • Workflow and infrastructure readiness
  • Organisational capability
  • Secure deployment
  • Governance processes
  • Human adoption
Speakers & Moderators

Conference Speakers & Panelists

Moderator

Conference Moderator

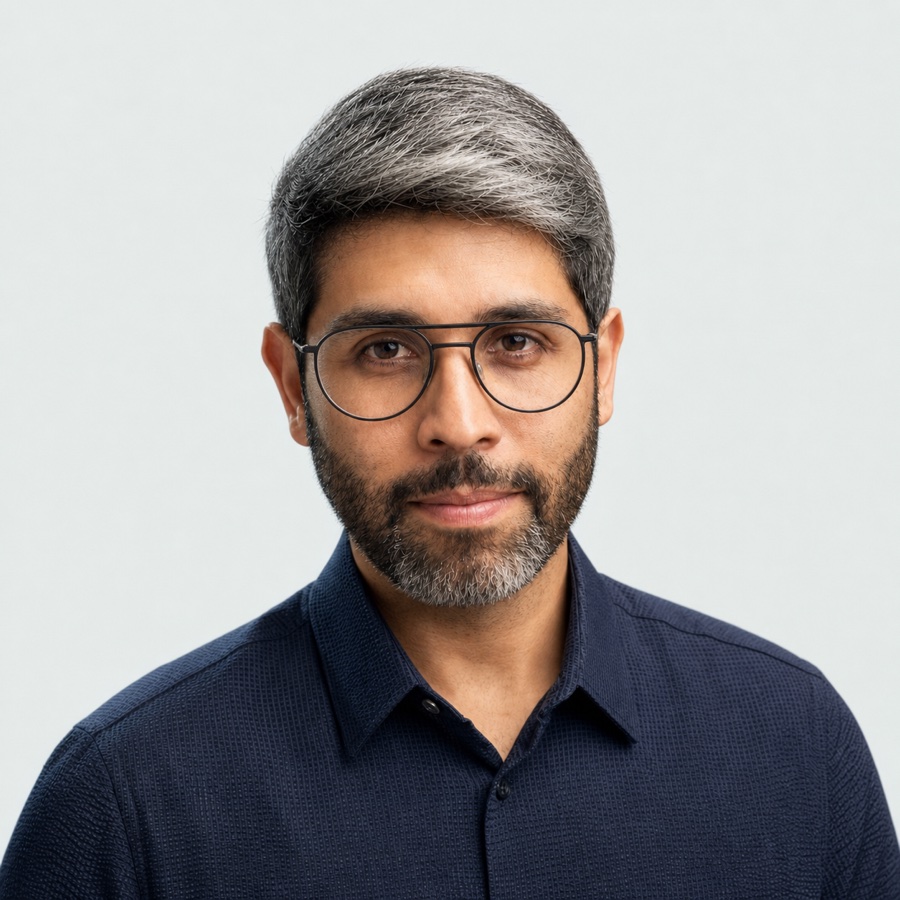
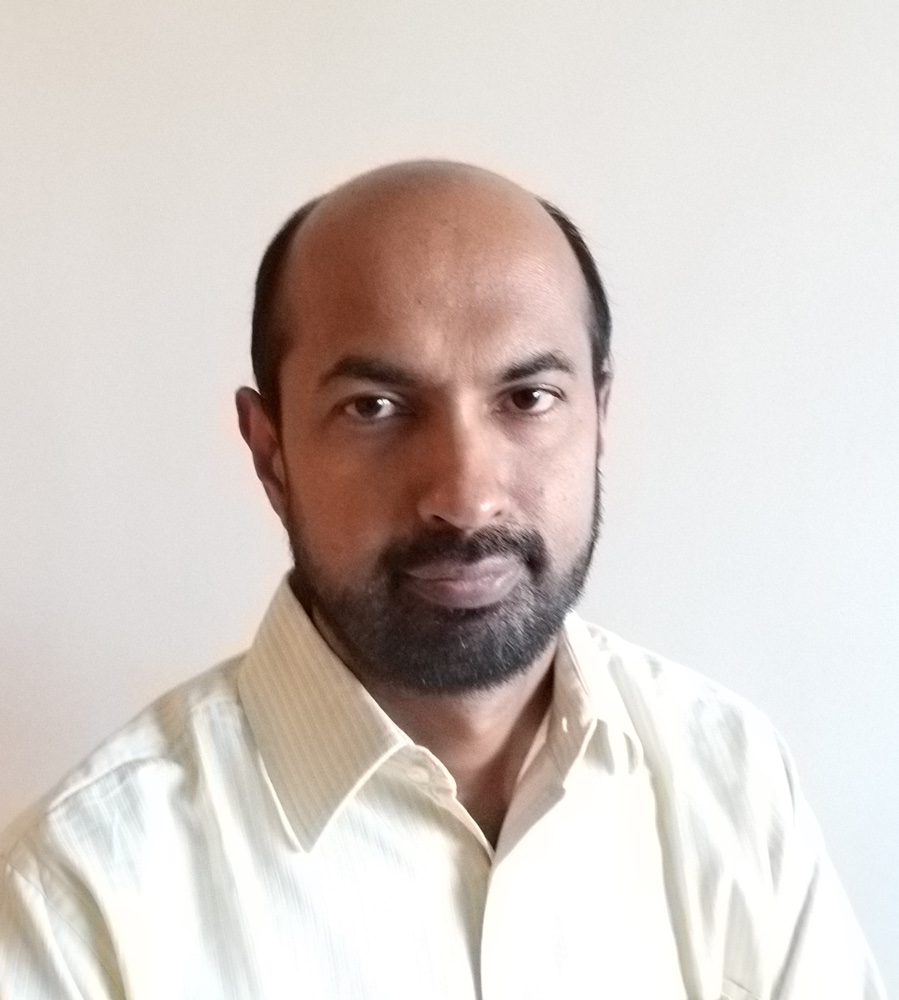
Nitin Dhavate

Nitin Dhavate

Data Privacy & AI Governance Head – Asia Pacific, Middle East & Africa (APMA) and Global Health

  • AI Governance
  • Data Privacy
  • Responsible AI
  • AI & Privacy Risk Management
  • Governance Programme Design & Implementation
  • Enterprise AI Governance

Nitin is a privacy, security and AI governance professional with a focus on planning, implementing and maintaining privacy and AI governance programs to enable business growth while managing privacy and AI risks.

Nitin is currently the Data Privacy and AI Governance Head for Novartis Asia Pacific, Middle East and Africa, across all the business functions and units. He also works on global initiatives at Novartis.

Theme 3

Governance, Accountability & Human Oversight

Cesar Said Rosales Torres
Cesar Said Rosales Torres organisation logo

Cesar Said Rosales Torres

Founder & Director, OuiCheck

Proposed Topic

Governing Increasingly Autonomous AI: Rethinking the Infrastructure for Autonomy

How emerging forms of AI autonomy are challenging traditional approaches to governance and human oversight, and what new infrastructure for authority, attention, assurance, and accountability may be needed to scale them responsibly.

César Rosales is the Founder and Director of OuiCheck, an AI assurance and advisory firm specializing in regulatory compliance, risk management, responsible AI, and the evaluation of AI systems for organizations across Europe and Latin America. OuiCheck helps organizations translate emerging AI regulation and responsible AI frameworks into practical approaches for managing risk, demonstrating trustworthiness, and scaling AI responsibly.

Over the past six years, he has served as an external advisor to the Inter-American Development Bank’s innovation laboratory, IDB Lab, on responsible AI, innovation, and venture ecosystems, where he coordinated and co-led fAIr LAC, an initiative focused on advancing the responsible adoption of AI among entrepreneurs, startups, and venture capital funds across Latin America and the Caribbean. He currently serves as an external consultant to the Inter-American Development Bank’s Technology and Transformation Department (TTD), focusing on AI governance and the responsible adoption of AI.

His work and research have also focused on algorithmic discrimination, AI governance, and the impact of emerging technologies on fundamental rights. He currently teaches on the impact of technology on fundamental rights in the Master in Technology and Global Affairs at IE University in Spain.

César holds a Master’s degree in Latin American Studies from Georgetown University, with a concentration in Political Economy, and a Bachelor’s degree in International Relations from Tecnológico de Monterrey in Mexico.

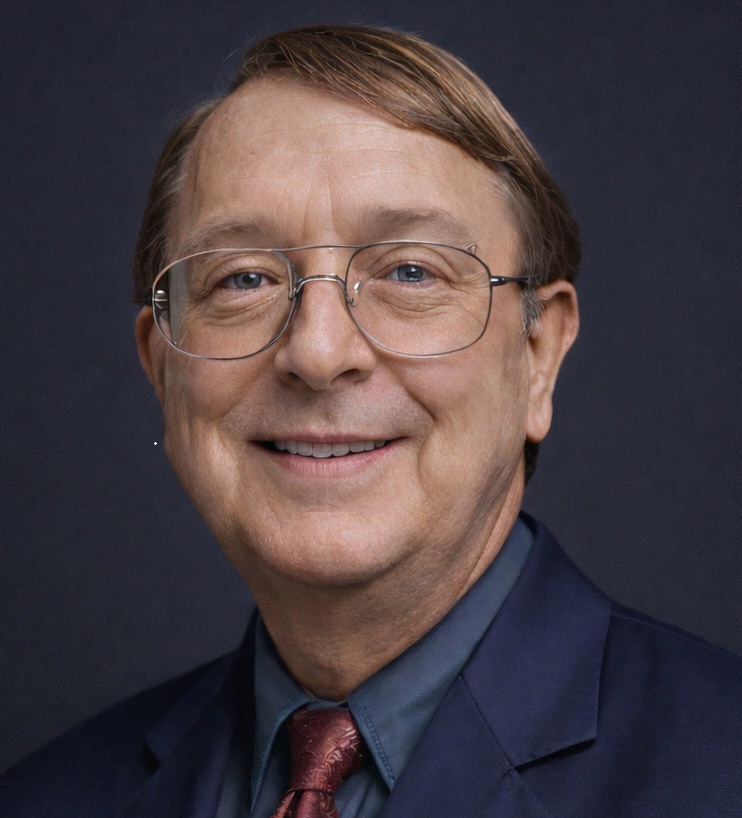
John M. Willis

John M. Willis

Founder & Chief Innovation Officer, Sustainable Future Tech, Inc.

Proposed Topic

Beyond Guardrails: Governing Agentic AI at the Point of Action

The presentation will examine why governing agentic AI requires more than behavioral guardrails and policy declarations. It will introduce deterministic runtime governance as the means of establishing enforceable authorization, controlling consequential actions, incorporating human oversight where required, and preserving independently verifiable evidence of governance decisions and execution.

John M. Willis is Founder and Chief Innovation Officer of Sustainable Future Tech, Inc., and a cybersecurity architect, AI governance researcher, and author specializing in the secure engineering of autonomous systems.

He is the creator of Runtime Governance Engineering, an approach to translating governance requirements into enforceable controls over consequential actions performed by AI agents and other automated systems.

His research focuses on deterministic authorization and enforcement at the point of execution, including agent identity, authority, policy constraints, system invariants, evidence integrity, and accountable human oversight. He is the principal architect of the AI Governance Control Plane (AGCP), a framework for separating probabilistic AI reasoning from authoritative execution decisions.

His publications include Runtime Governance Engineering: Foundations and Architecture—From Governance Intent to Controlled Execution, along with research on runtime execution governance, formal execution semantics, and secure AI architecture.

His professional background spans enterprise cybersecurity architecture, federal cybersecurity programs, systems engineering, and emerging technologies. His work emphasizes moving AI governance beyond documented policies and behavioral guardrails toward independently verifiable, enforceable controls over consequential system behavior.

Expected Outcomes

The event is expected to:

The Agentic Systems Framework will create a practical bridge between AI capability and responsible institutional implementation. By bringing together leaders from technology, cybersecurity, governance, policy, research, and the public sector, the event will help clarify what organisations need in order to deploy increasingly autonomous AI systems with appropriate trust, security, accountability, and human oversight.

  • build a clearer shared understanding of how Agentic AI differs from conventional assistive AI and what greater autonomy means in operational settings;

  • identify practical readiness gaps organisations may encounter when moving Agentic AI from experimentation into operational environments;

  • improve understanding of security approaches for agent identity, permissions, runtime monitoring, containment, recovery, and operational resilience;

  • surface emerging governance approaches for accountability, decision authority, human approval, auditability, and continuous assurance;

  • highlight implementation experiences and practical lessons that can inform responsible Agentic AI adoption across sectors;

  • strengthen dialogue between technology, security, governance, policy, research, and public-sector stakeholders on the responsible deployment of autonomous AI systems;

  • support continued knowledge exchange and potential follow-up collaboration around trustworthy, secure, and governable Agentic AI.

Who Should Attend

The event is designed for leaders and professionals involved in shaping, implementing, securing, governing, or evaluating AI-enabled systems, including:

  • CIOs, CTOs, CISOs, Chief Digital Officers and Senior Technology Leaders

  • AI, Data and Digital Transformation Leaders

  • Cybersecurity and Information Security Professionals

  • AI Governance, Risk, Compliance, Privacy and Assurance Leaders

  • Enterprise Architecture Leaders

  • Enterprise Technology and Innovation Leaders

  • Policy, Governance and Public-Sector Technology Professionals

  • Researchers, AI Specialists and Institutional Decision-Makers

  • Institutional and Public-Sector Technology Leaders

  • Professionals responsible for AI implementation and operational transformation

Schedule / Timeline

Thursday

21January
2027

Time
5:30 pm - 8:30 pm UAE Time
Format
Virtual Event on Zoom
  1. 5:30 pm Programme opens

  2. Opening Remarks and Context Setting

    1 moderator

  3. Opening Keynote

    The Agentic Systems Framework: Trust, Security, and Governance

  4. Theme 1

    AI Autonomy & Decision-Making

    2 panelists, 15 minutes each

  5. Theme 2

    Security & Resilience of Autonomous AI

    2 panelists, 15 minutes each

  6. Theme 3

    Governance, Accountability & Human Oversight

    2 panelists, 15 minutes each

  7. Interactive Live Q&A

    Audience discussion with the speakers

  8. Closing Reflections and Key Takeaways

    Emerging practices and areas for continued dialogue

  9. 8:30 pm Close

Sponsors

Sponsorship Opportunities

Partner with The Agentic Systems Framework to position your organisation alongside a focused community of leaders shaping the future of artificial intelligence, autonomous systems, cybersecurity, governance, and digital transformation.

Become a Sponsor

Sponsorship Benefits

  • Brand visibility across an AI and technology-focused audience
  • Positioning alongside industry leaders and subject-matter experts
  • Speaking / participation opportunities
  • Engagement with senior decision-makers and stakeholders
  • Association with responsible innovation, trustworthy AI, and agentic systems

Register

Join the Conference

Join The Agentic Systems Framework: Trust, Security, and Governance on 21 January 2027 and be part of a focused global conversation on responsible agentic AI adoption.

Participation is free, but registration is required.

Contact Us

TecHive Association

Email:partnerships@techiveglobal.com

For:

  • Registration Queries
  • Sponsorship Opportunities
  • Speaker Participation
  • Partnership Enquiries
Subscribe to Our Newsletter

Stay updated with latest insights & events

Next
Home
Stay connected! Follow TecHive on social media for updates and success stories.